零知识证明 Diffie-Hellman 密钥交换
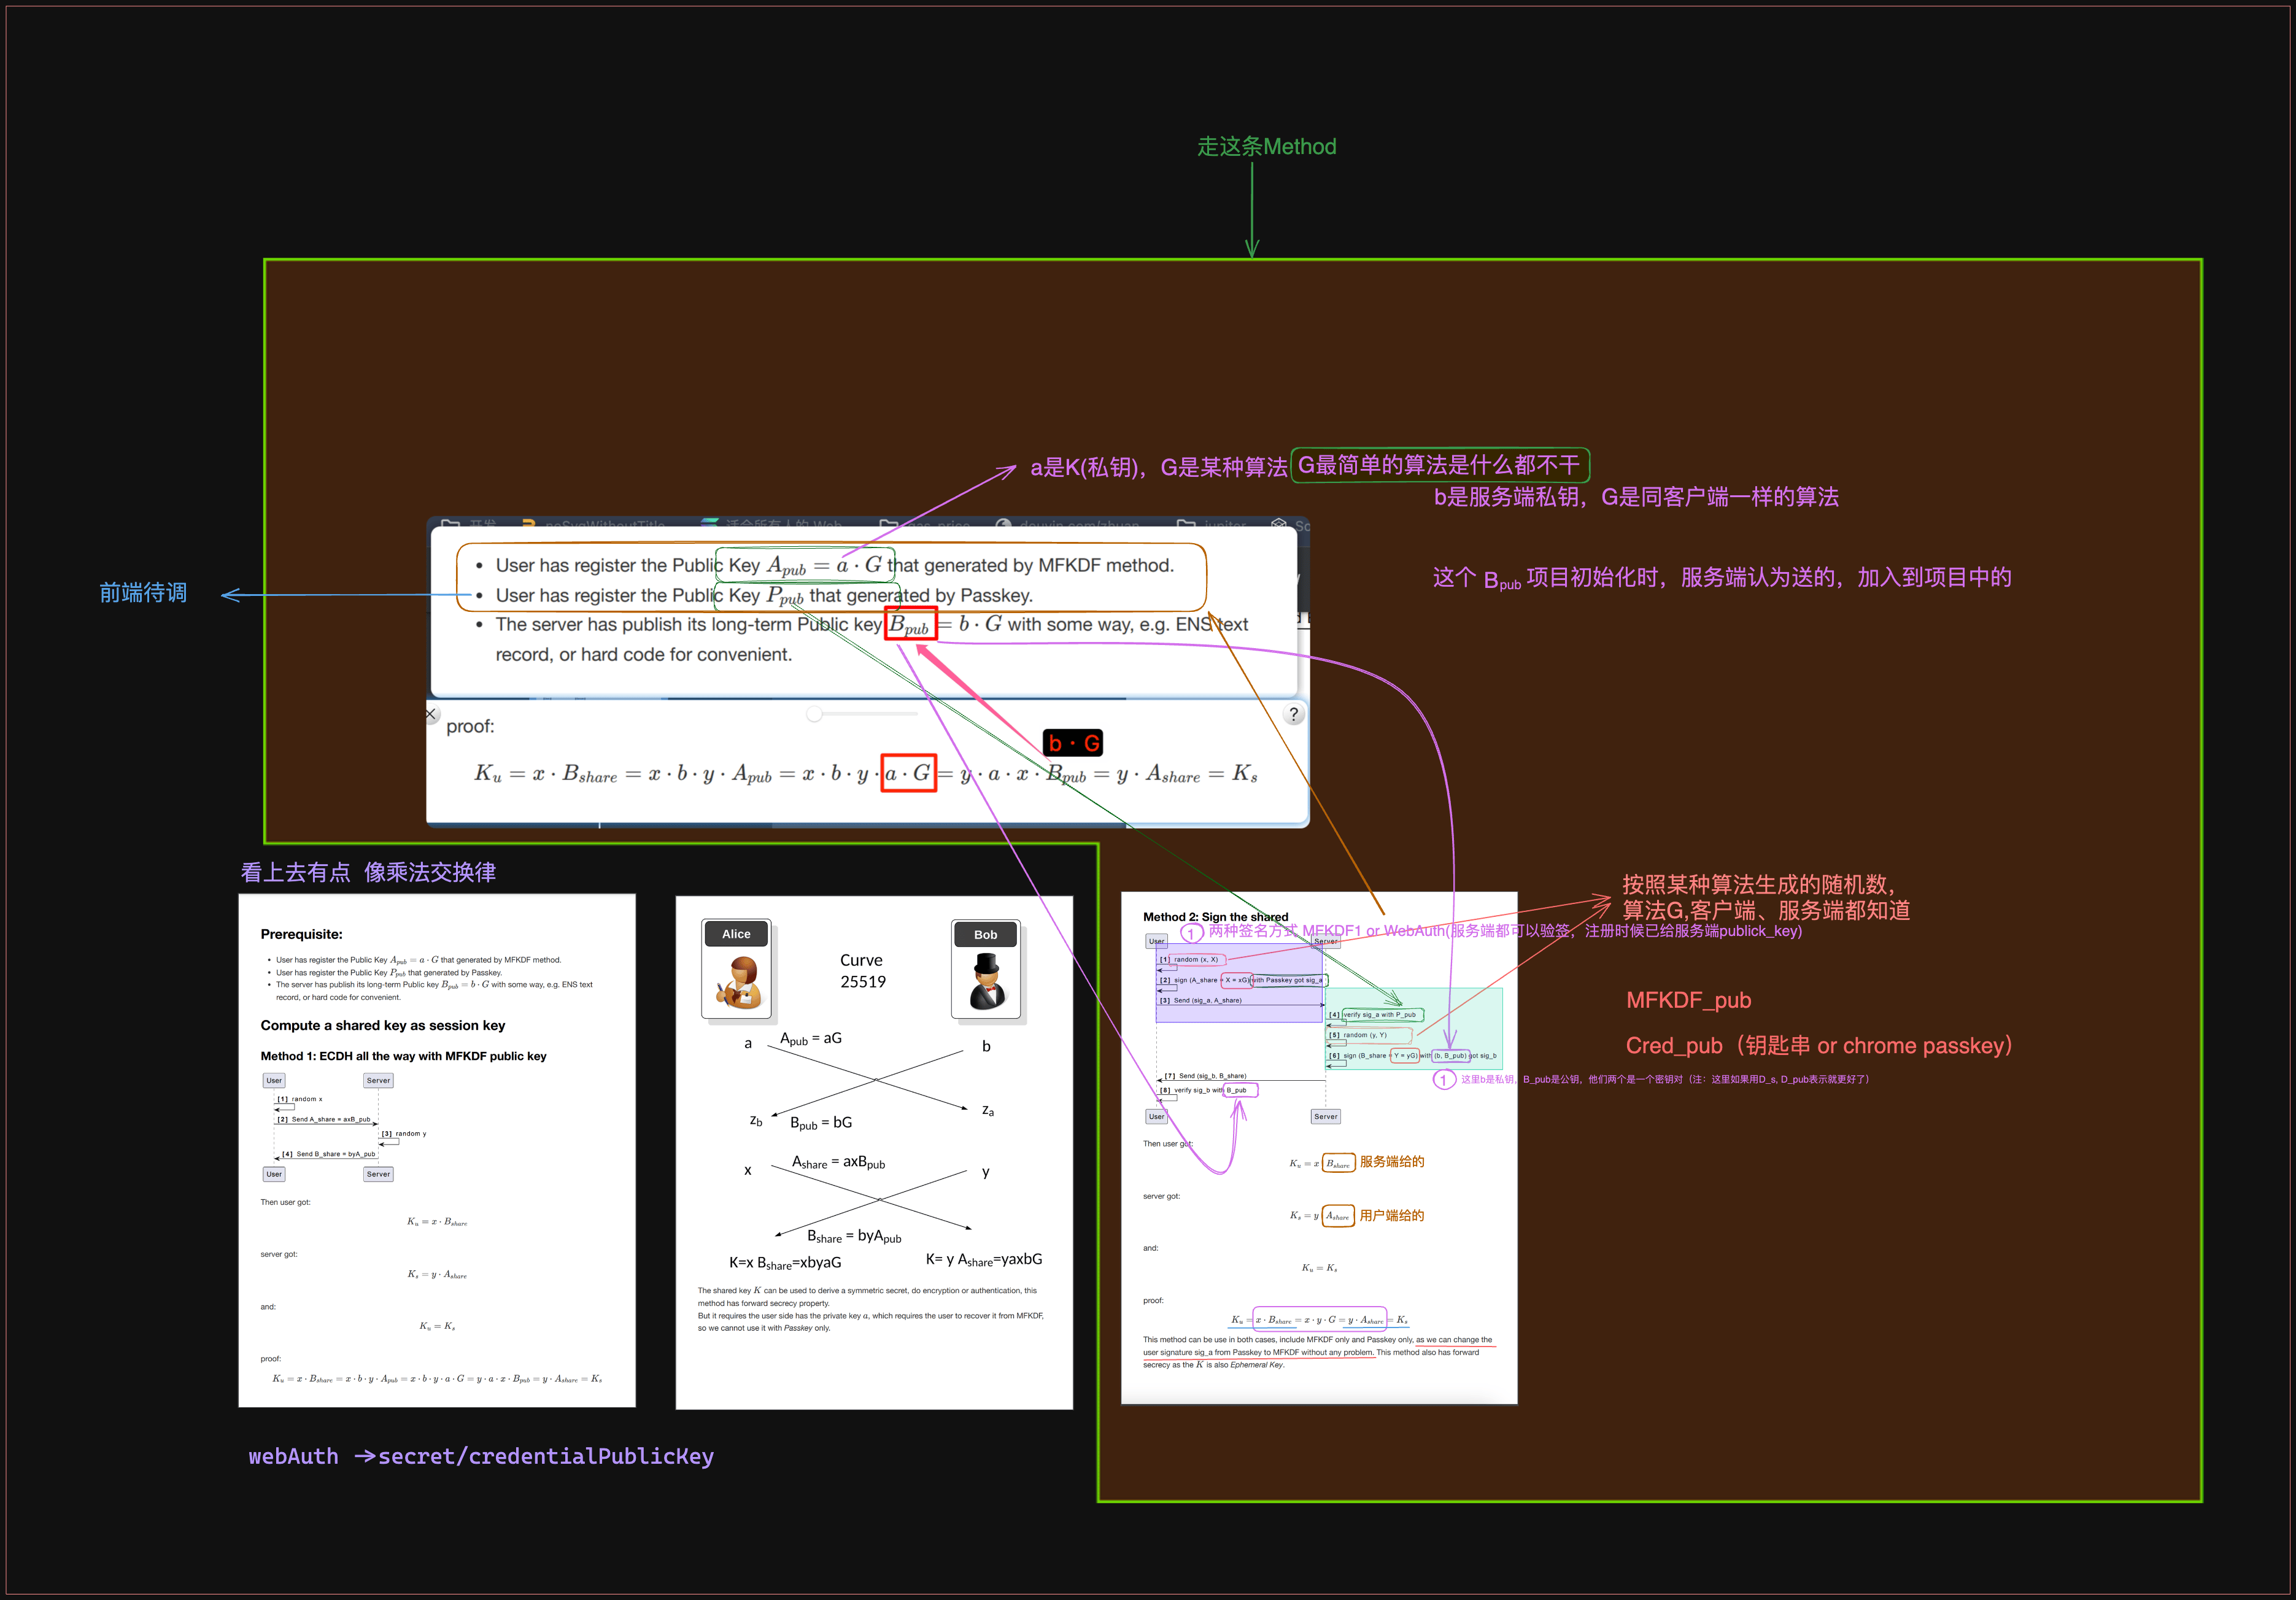
Prerequisite:
- User has register the Public Key that generated by MFKDF method.
- User has register the Public Key that generated by Passkey.
- The server has publish its long-term Public key with some way, e.g. ENS text record, or hard code for convenient.
Compute a shared key as session key
Method 1: ECDH all the way with MFKDF public key
Then user got:
server got:
and:
proof:
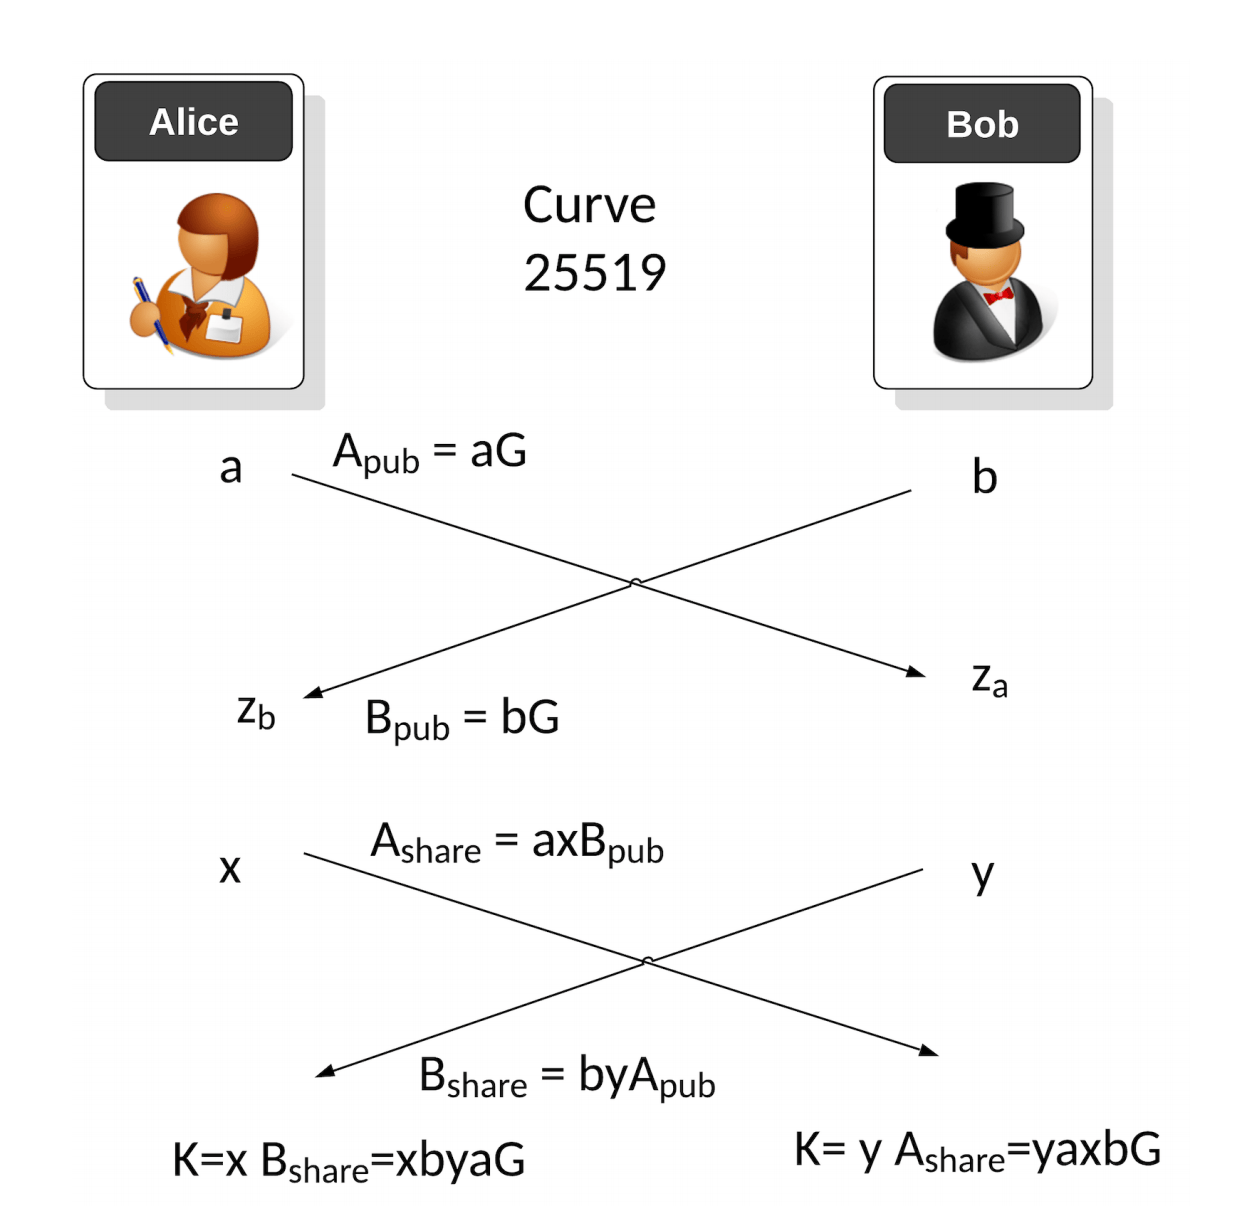
The shared key can be used to derive a symmetric secret, do encryption or authentication, this method has forward secrecy property. But it requires the user side has the private key , which requires the user to recover it from MFKDF, so we cannot use it with Passkey only.
Method 2: Sign the shared
Then user got:
server got:
and:
proof:
This method can be use in both cases, include MFKDF only and Passkey only, as we can change the user signature sig*a from Passkey to MFKDF without any problem. This method also has forward secrecy as the is also Ephemeral Key.
proof 推导
为了证明在 Diffie-Hellman 密钥交换协议中,双方计算出的共享密钥是相同的,我们可以通过数学推导来展示这一点。以下是详细的证明过程:
参数设定
- 选择一个大素数 和一个生成元 (这些参数是公开的)。
- 用户 A 选择一个私有随机数 作为私钥,并计算 作为公钥。
- 用户 B 选择一个私有随机数 作为私钥,并计算 作为公钥。
交换公钥
- 用户 A 将公钥 发送给用户 B。
- 用户 B 将公钥 发送给用户 A。
计算共享密钥
- 用户 A 使用用户 B 的公钥 和自己的私钥 计算共享密钥: 。
- 用户 B 使用用户 A 的公钥 和自己的私钥 计算共享密钥: 。
证明共享密钥相同
我们需要证明 ,即用户 A 和用户 B 计算出的共享密钥是相同的。
-
用户 A 计算共享密钥 :
其中 ,因此:
根据模运算的性质 (乘法和幂) ,可以得到:
-
用户 B 计算共享密钥 :
其中 ,因此:
同样地,根据模运算的性质,可以得到:
由于指数运算的交换性,即 ,因此:
结论
通过上述推导,我们证明了用户 A 和用户 B 计算出的共享密钥 和 是相同的,即:
因此,Diffie-Hellman 密钥交换协议能够确保双方在不安全的通信信道上安全地生成相同的共享密钥。这一共享密钥可以用于后续的加密通信,确保数据的机密性和完整性。